
It asks not just whether approval checkpoints exist but whether they’re designed so reviewers can actually make decisions rather than reflexively approve. As an implementation practice, retain the agent identity, task scope, commit, checks, and approval record. AI code review can investigate architectural fit and requirements using available context, then present findings for verification.
AI-generated code enters through many tools and IDEs, so a program built around one assistant misses the rest, and shadow AI usage slips past controls entirely. AI code governance works by embedding controls into the development lifecycle, so oversight happens as code is written and merged, catching problems before they ship. Follow the coding-agent policy implementation guide to turn the framework into repository settings. It handles the routine layer of https://event-miami24.com/software-development-for-energy-and-utility-asset-management.html review so senior engineers can spend their attention on decisions that actually require human judgment. CI checks and audit records provide evidence for that system; they do not cover the whole standard. Named owners, documented decisions, and review evidence can contribute to a team’s implementation.
The controls exist to protect that judgment and direct it where it counts. Developers feel governance as faster reviews and fewer surprises, while the audit trail builds itself in the background. Findings arrive with evidence and reasoning, and reading every line becomes the exception reserved for the changes where judgment genuinely matters. Standards get enforced by an automated first reviewer instead of a checklist, so most changes flow through without a human gatekeeper. Code review is one control inside governance rather than the whole of it.
Use the request changes workflow with repository protection to configure blocking behavior; retain deterministic tests and human approvals. CodeRabbit teams can add custom pre-merge checks with explicit criteria and inspect the evidence behind each result. https://pagemakers.net/the-benefits-of-outsourcing-for-small-businesses/ Configure required checks and approvals on the protected branch, and restrict bypass actors. Conftest evaluates structured configuration with policy rules. An agent that can open PRs across 200 repos but can’t touch infrastructure configs or push to protected branches is a governed agent. Without centralized governance, every team’s agent setup is its own policy island.
- Centralized governance, applied through shared rules in CI and a consistent review layer on every PR, is what collapses those policy islands into a single enforceable standard
- Use dedicated secret scanners, linters, and tests for the code properties they cover, and require human review for decisions needing product or architectural context.
- The four risks above all collapse to the same gap, which is the absence of an enforcement layer that runs at the speed agents ship code.
- Runtime enforcement sits between the agent and the systems it can touch, evaluating each file operation, API call, or shell command against this tiered policy before it executes.
Extend GitLab Duo Agent Platform into your business systems
Written instructions help communicate standards; reviewers and executable checks must still verify the output. Coding agents replicate the patterns they see in the codebase, including the inconsistent or suboptimal ones. Infrastructure changes need a separate authorization boundary. Each risk maps to a specific governance control that, if missing, lets the problem compound at the speed agents generate code. Without those limits enforced at runtime, the gap between policy and practice is exactly where the risks below take root.

A practical framework to implement

For authentication, infrastructure, and migration changes, the designated owner reviews test results and a rollback plan before authorizing release. For repository setup and a worked policy example, use AI governance for coding agents. See where AI tools generate code, correlate commits with risk signals, and maintain visibility across your AI software supply chain.
It’s also distinct from application security (AppSec), which catches vulnerability patterns in code that already exists. Inside the SDLC, that means governing coding agents that write PRs, modify configs, and ship code into production. The PR can still propose the change, but an infrastructure owner must review the plan and authorize the deployment through the release workflow. Its development credentials should prevent applying that policy.
AI-generated code introduces new risks around security vulnerabilities, licensing compliance, and architectural drift. A framework for establishing quality, security, and compliance checks to manage the risks of AI-assisted development without sacrificing velocity. This guide provides actionable steps to implement scanning, create audit trails, and define approval workflows.
Superblocks: best for governing AI-generated apps
Gain visibility into AI-generated code, correlate risk at commit, and govern AI-assisted development — so organizations can adopt AI coding with confidence. Introducing Citizen AI — AI literacy training for every employee, not just developers. How do I avoid creating governance that kills developer velocity?
How does AI code governance work?
It requires continuous measurement and improvement based on real-world data. Define clear rules for when human approval is required. Establishing governance for AI-generated code requires moving beyond traditional code review. Crucially, log all AI actions and model versions used to generate code, creating a digital provenance trail. Automate initial scans to catch common issues, routing only high-risk or anomalous outputs for human review. The goal is to create a Human-in-the-Loop (HITL) Governance System that provides oversight without becoming a bottleneck for developers.
Highlight elevated risk patterns and provide governance insights aligned with secure coding policies. Identify unsanctioned AI tools operating outside approved governance policies. Gain visibility into which AI tools contribute code — creating a verifiable AI SBOM. It connects AI usage visibility, risk intelligence, and developer capability insights across the software development lifecycle.
How AI code governance relates to neighboring practices
This policy becomes the foundation for all automated governance checks and team training, ensuring consistency and reducing risk from the outset. An AI code policy is a living document that defines the acceptable use, quality standards, and security requirements for all AI-assisted development. This document sets the rules of the road, aligning your team on quality, security, and compliance before a single line of code is generated. Establishing a formal policy is the critical first step in governing AI-generated code.


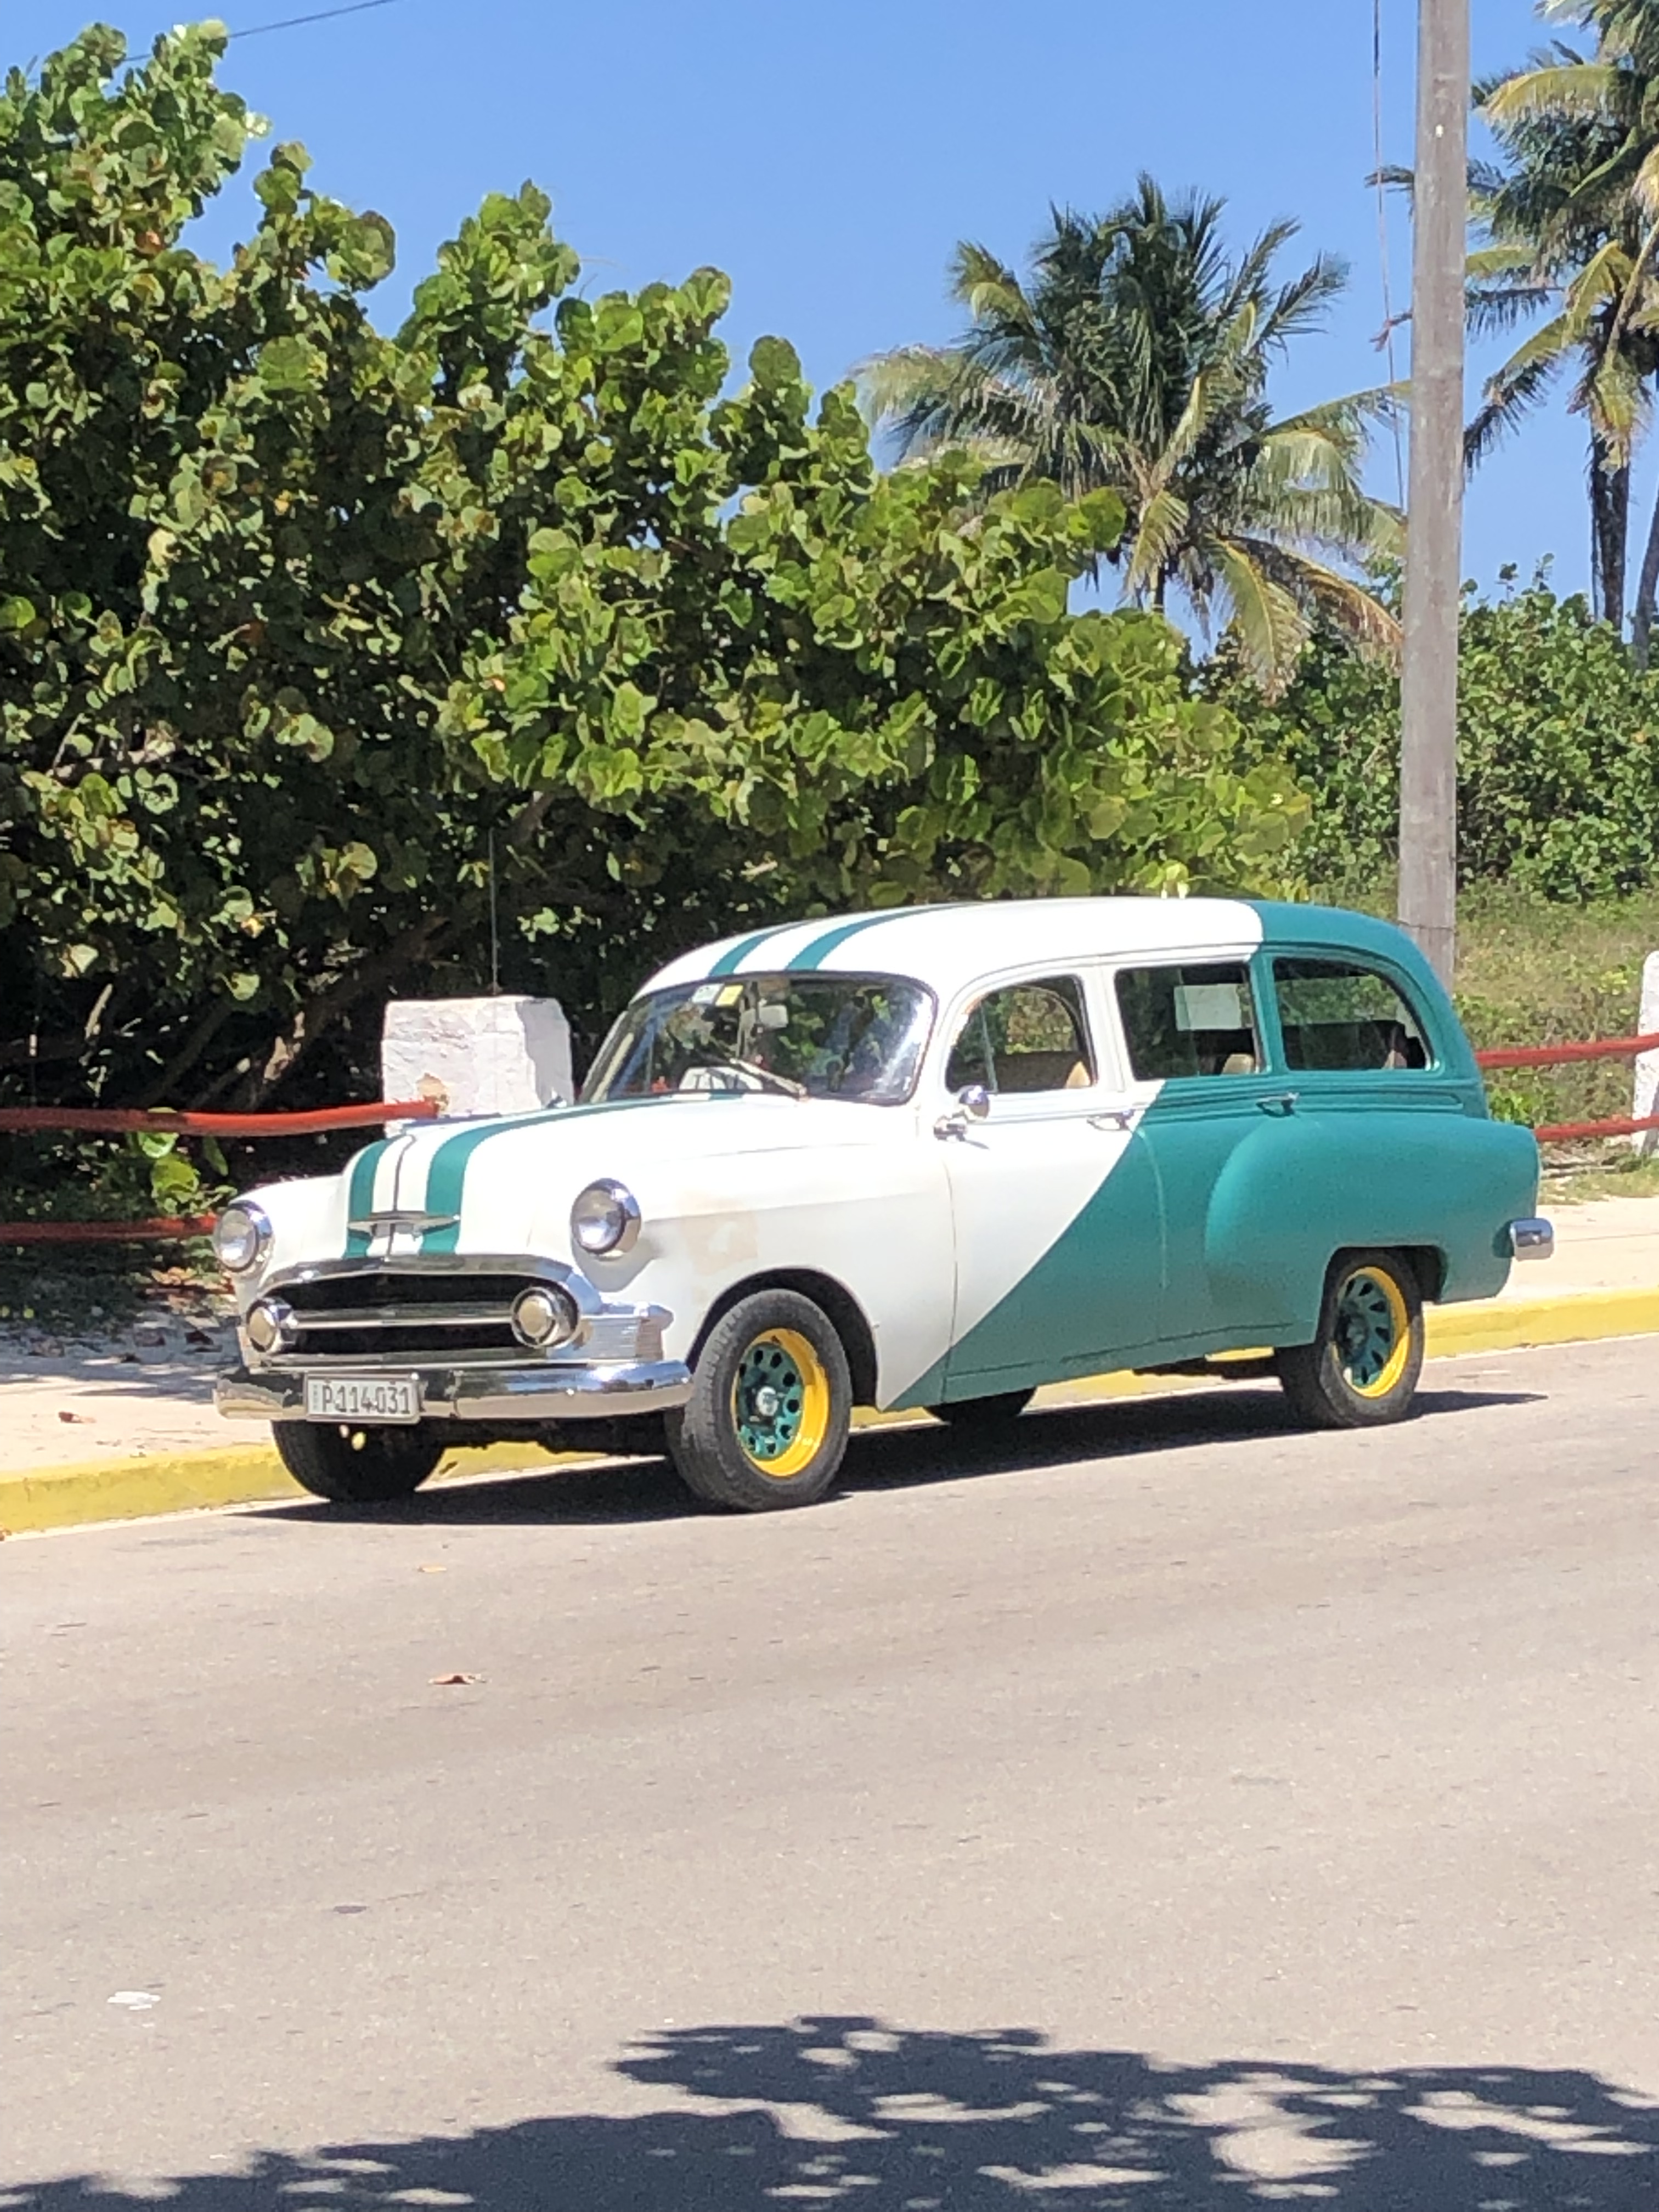

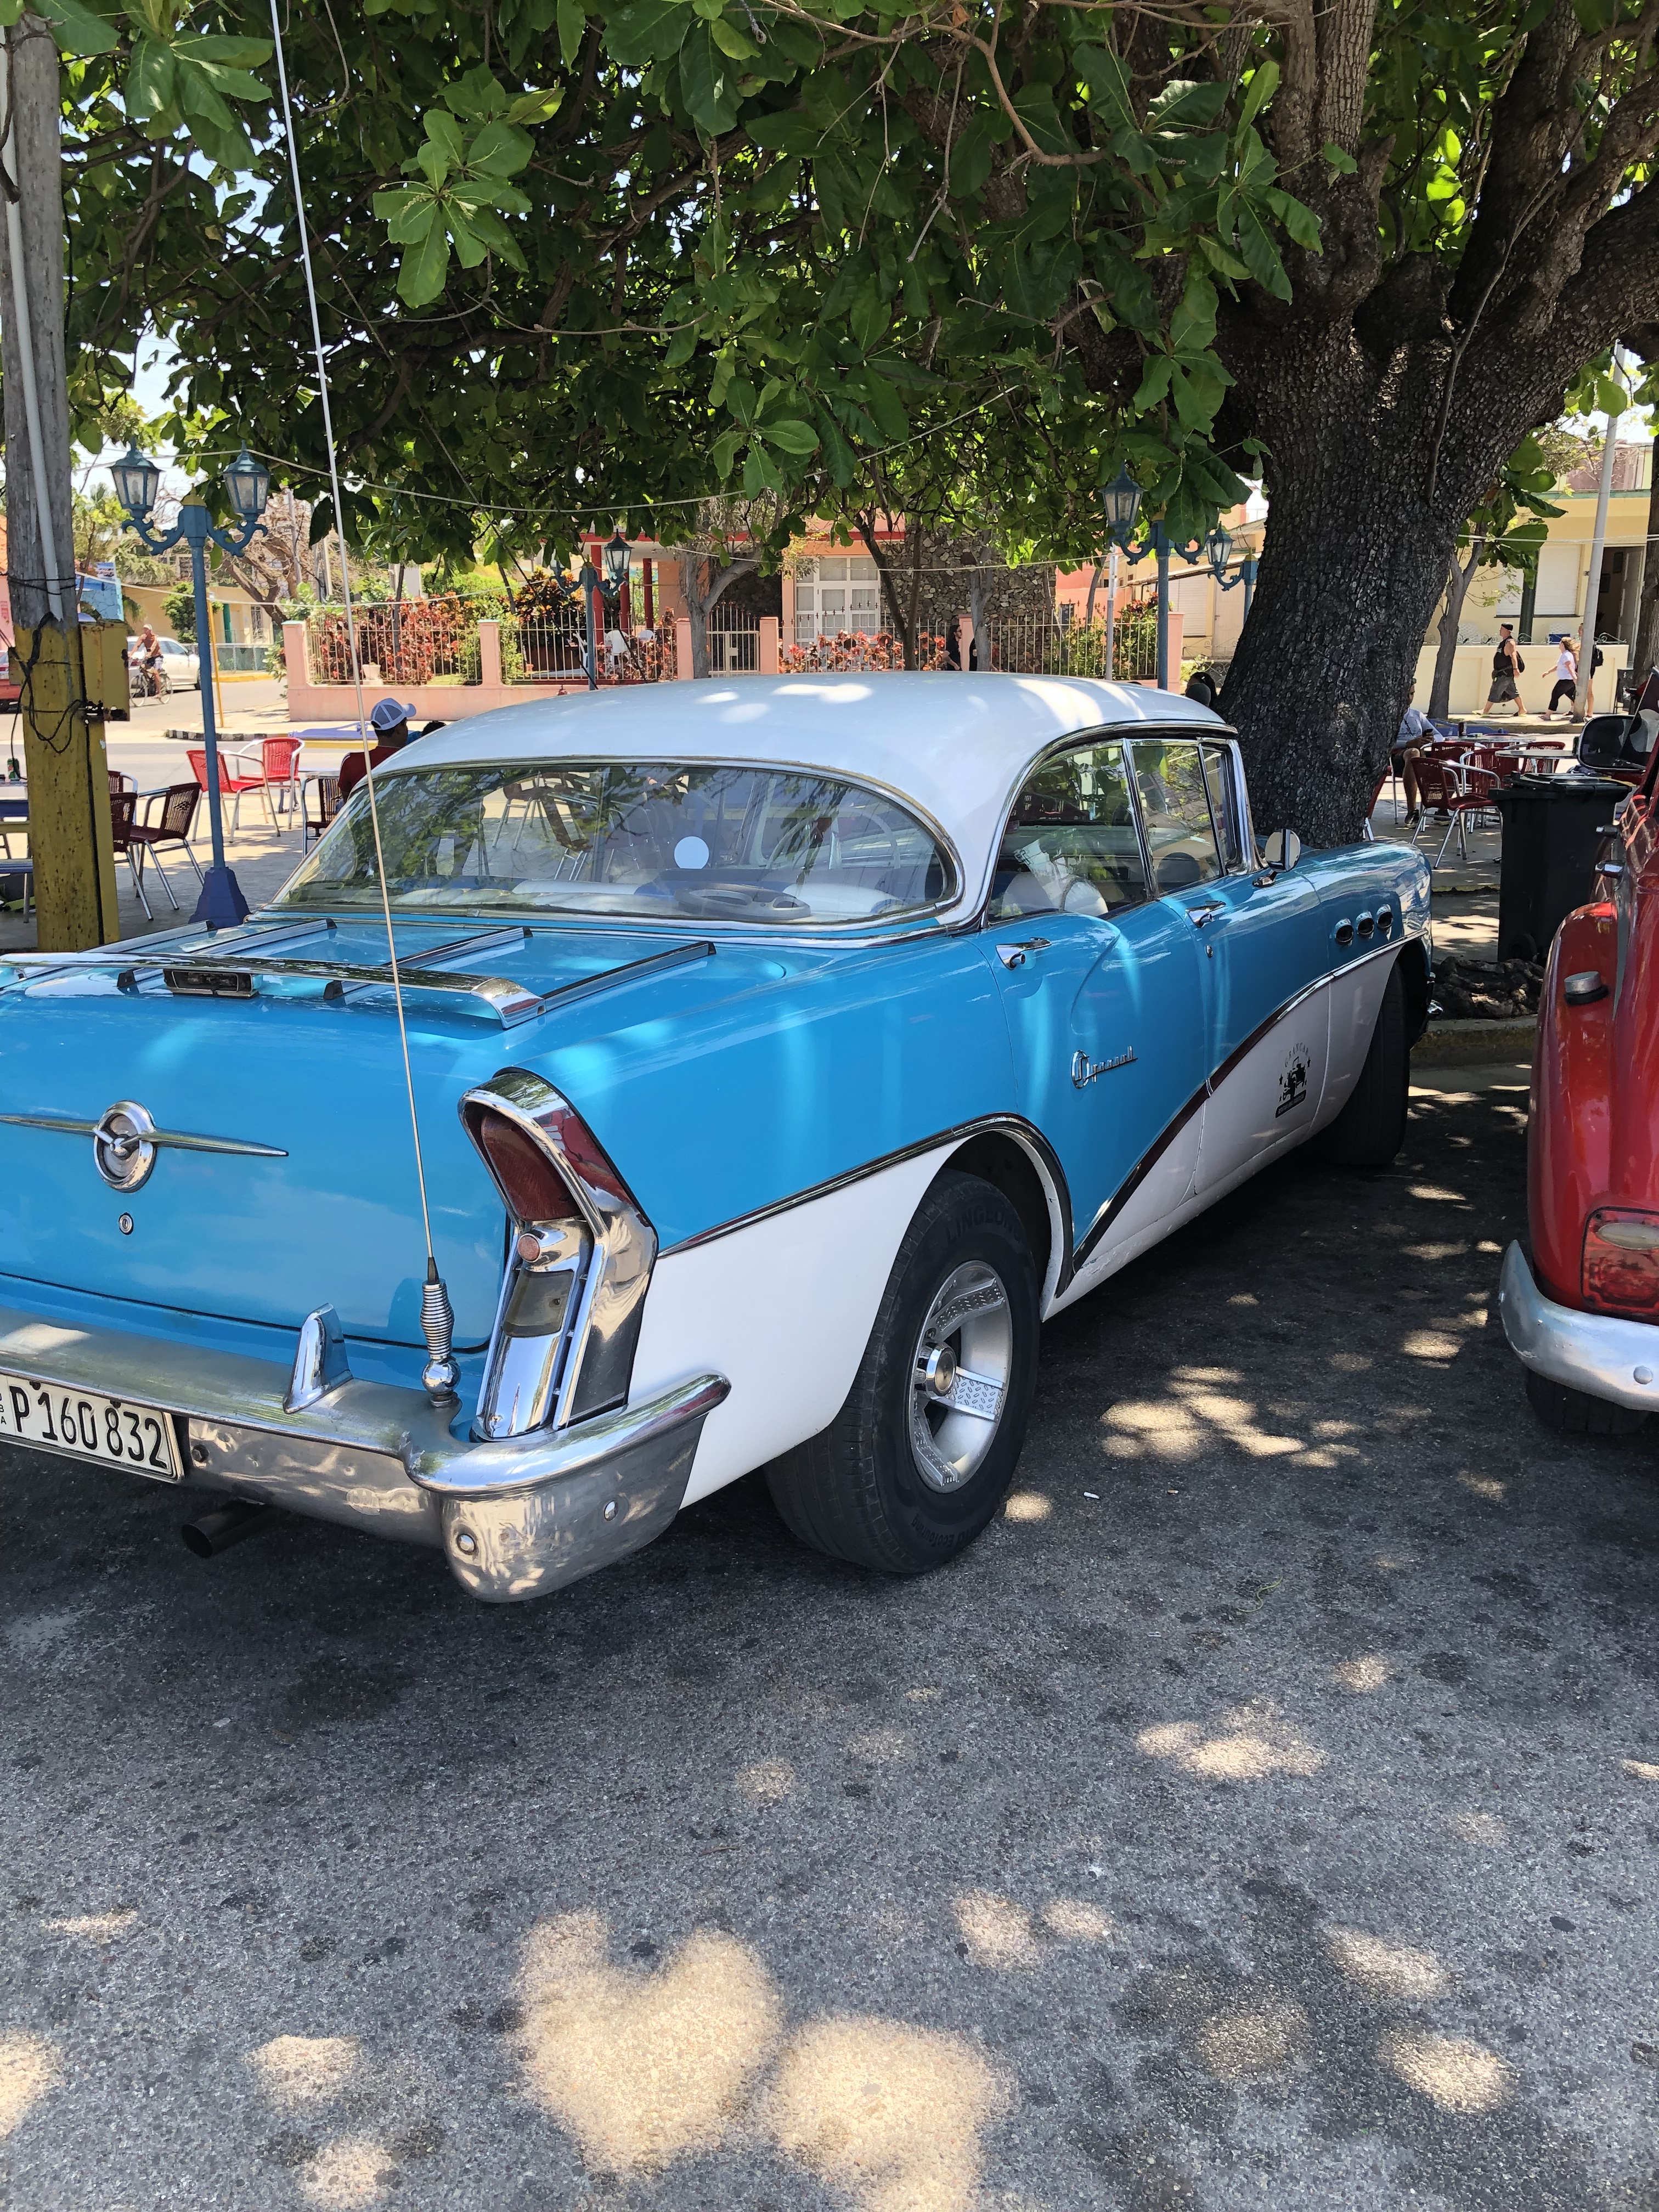
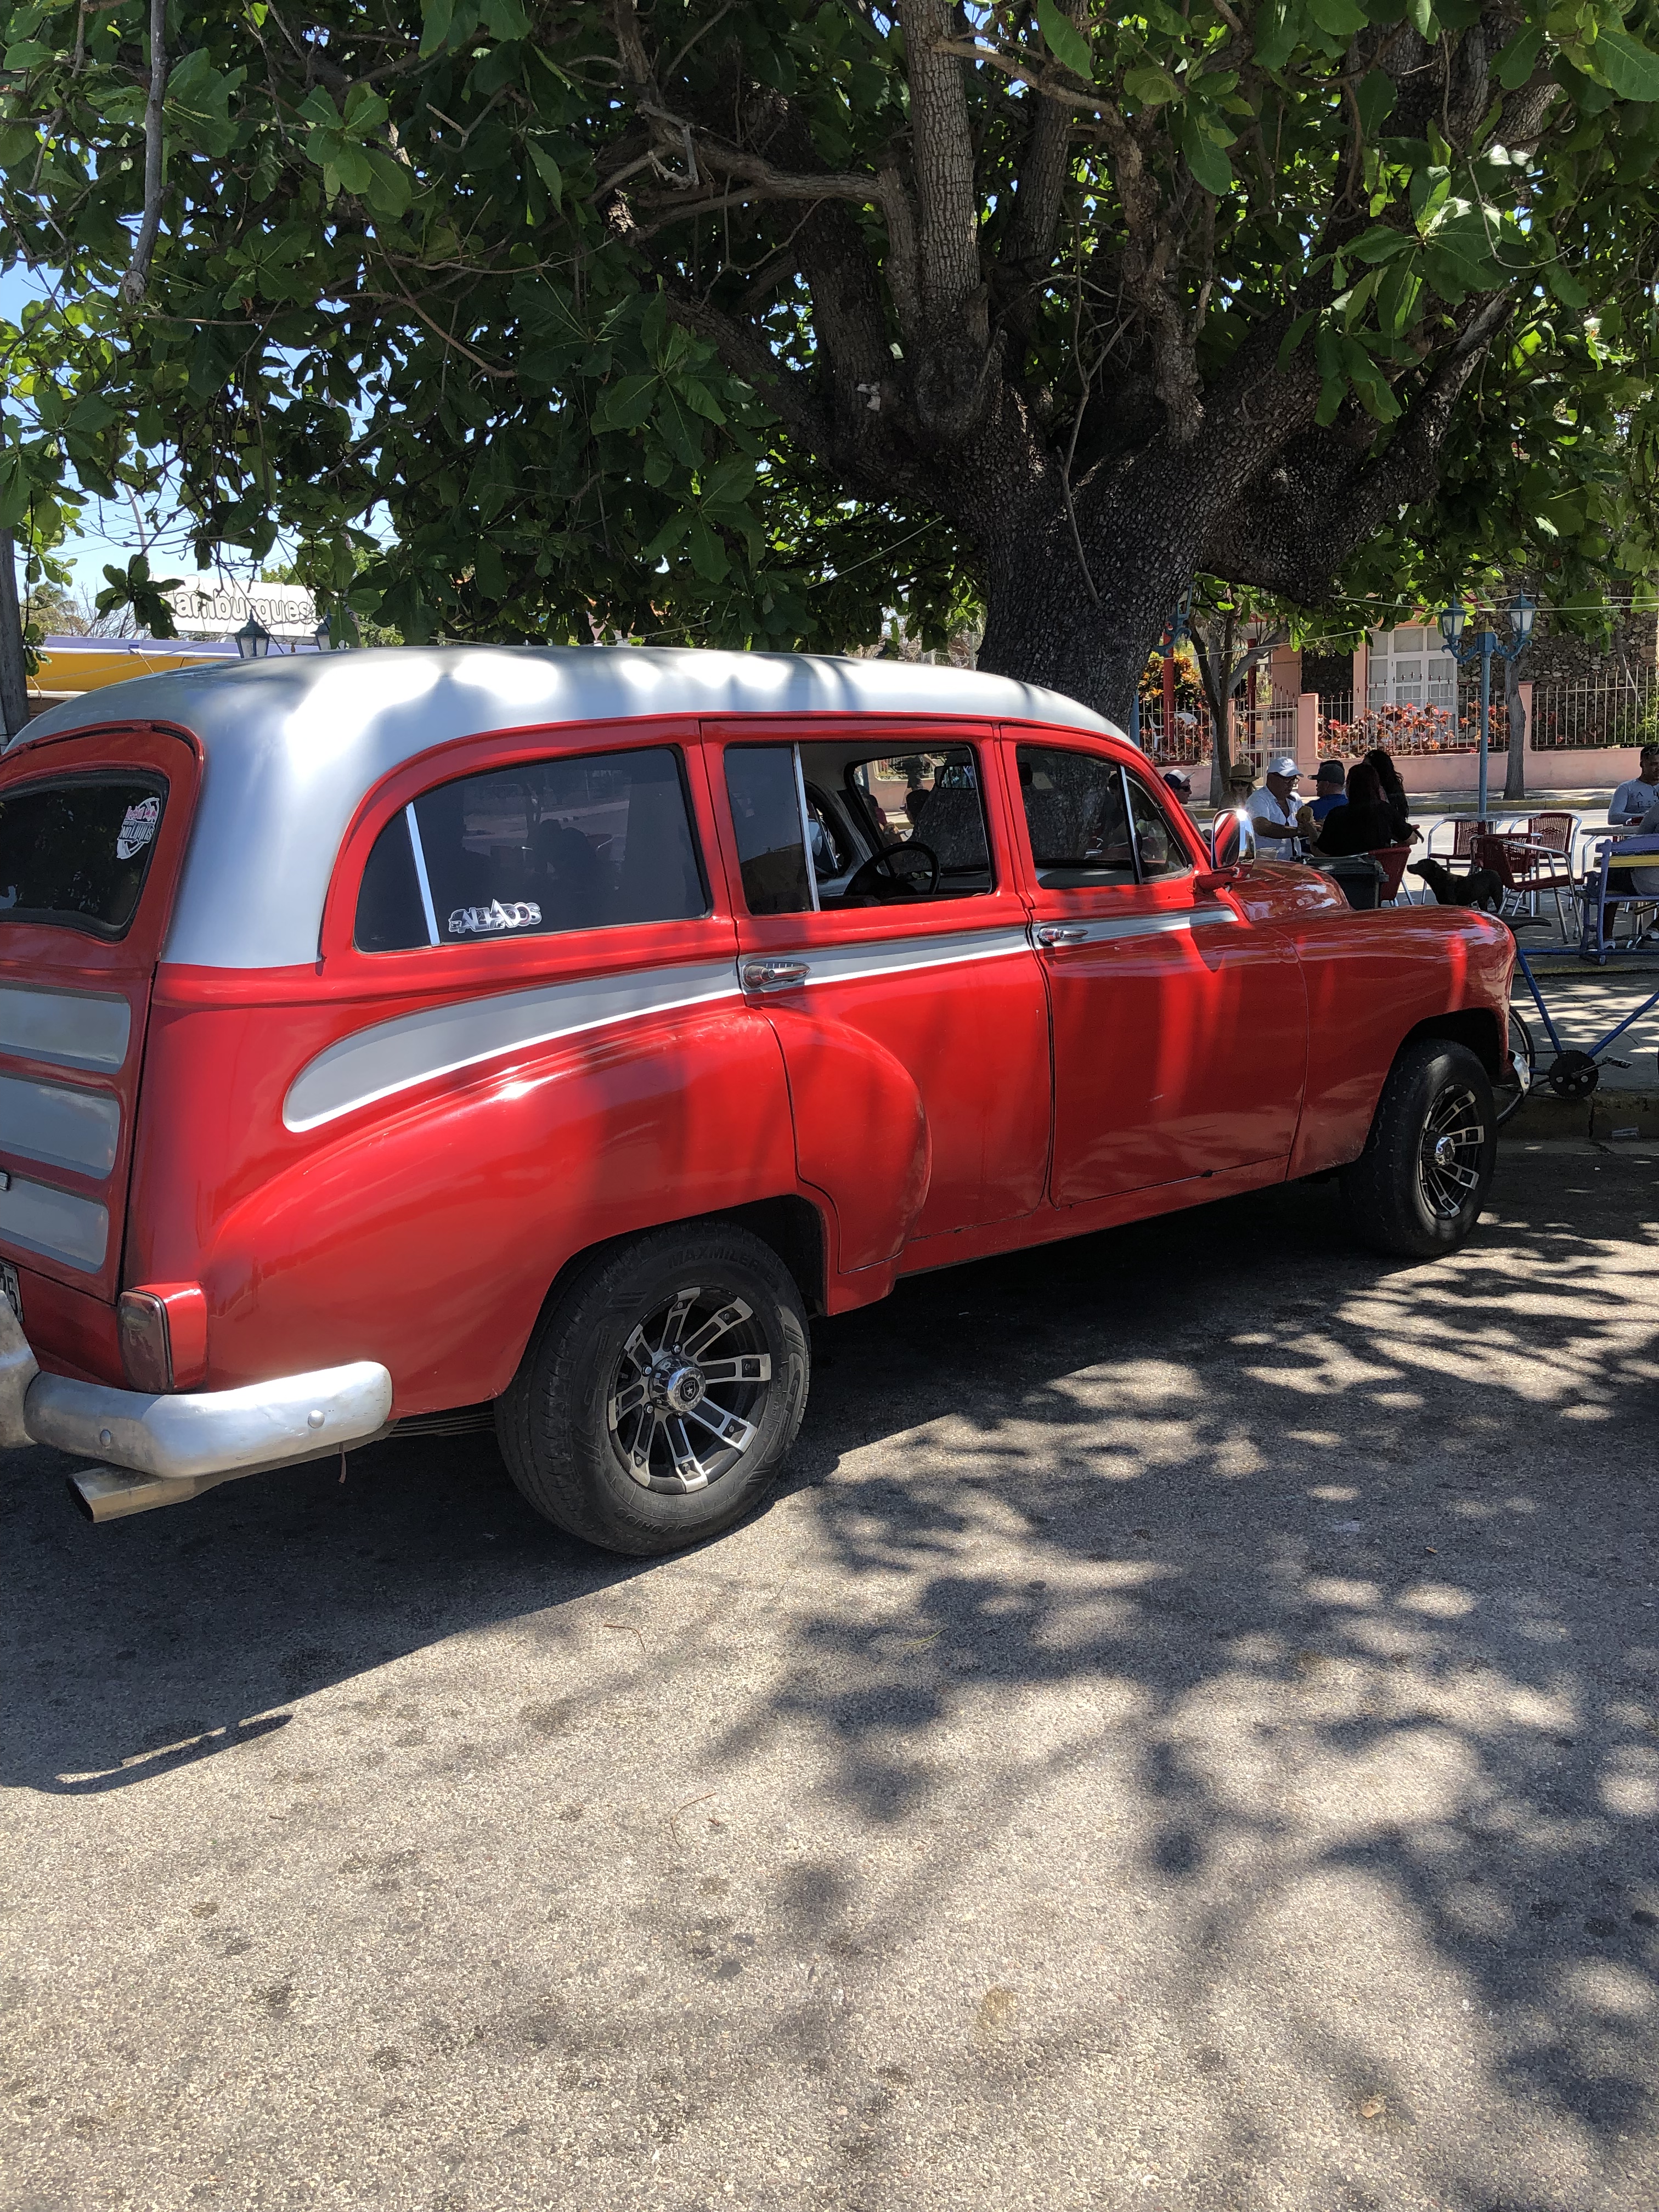
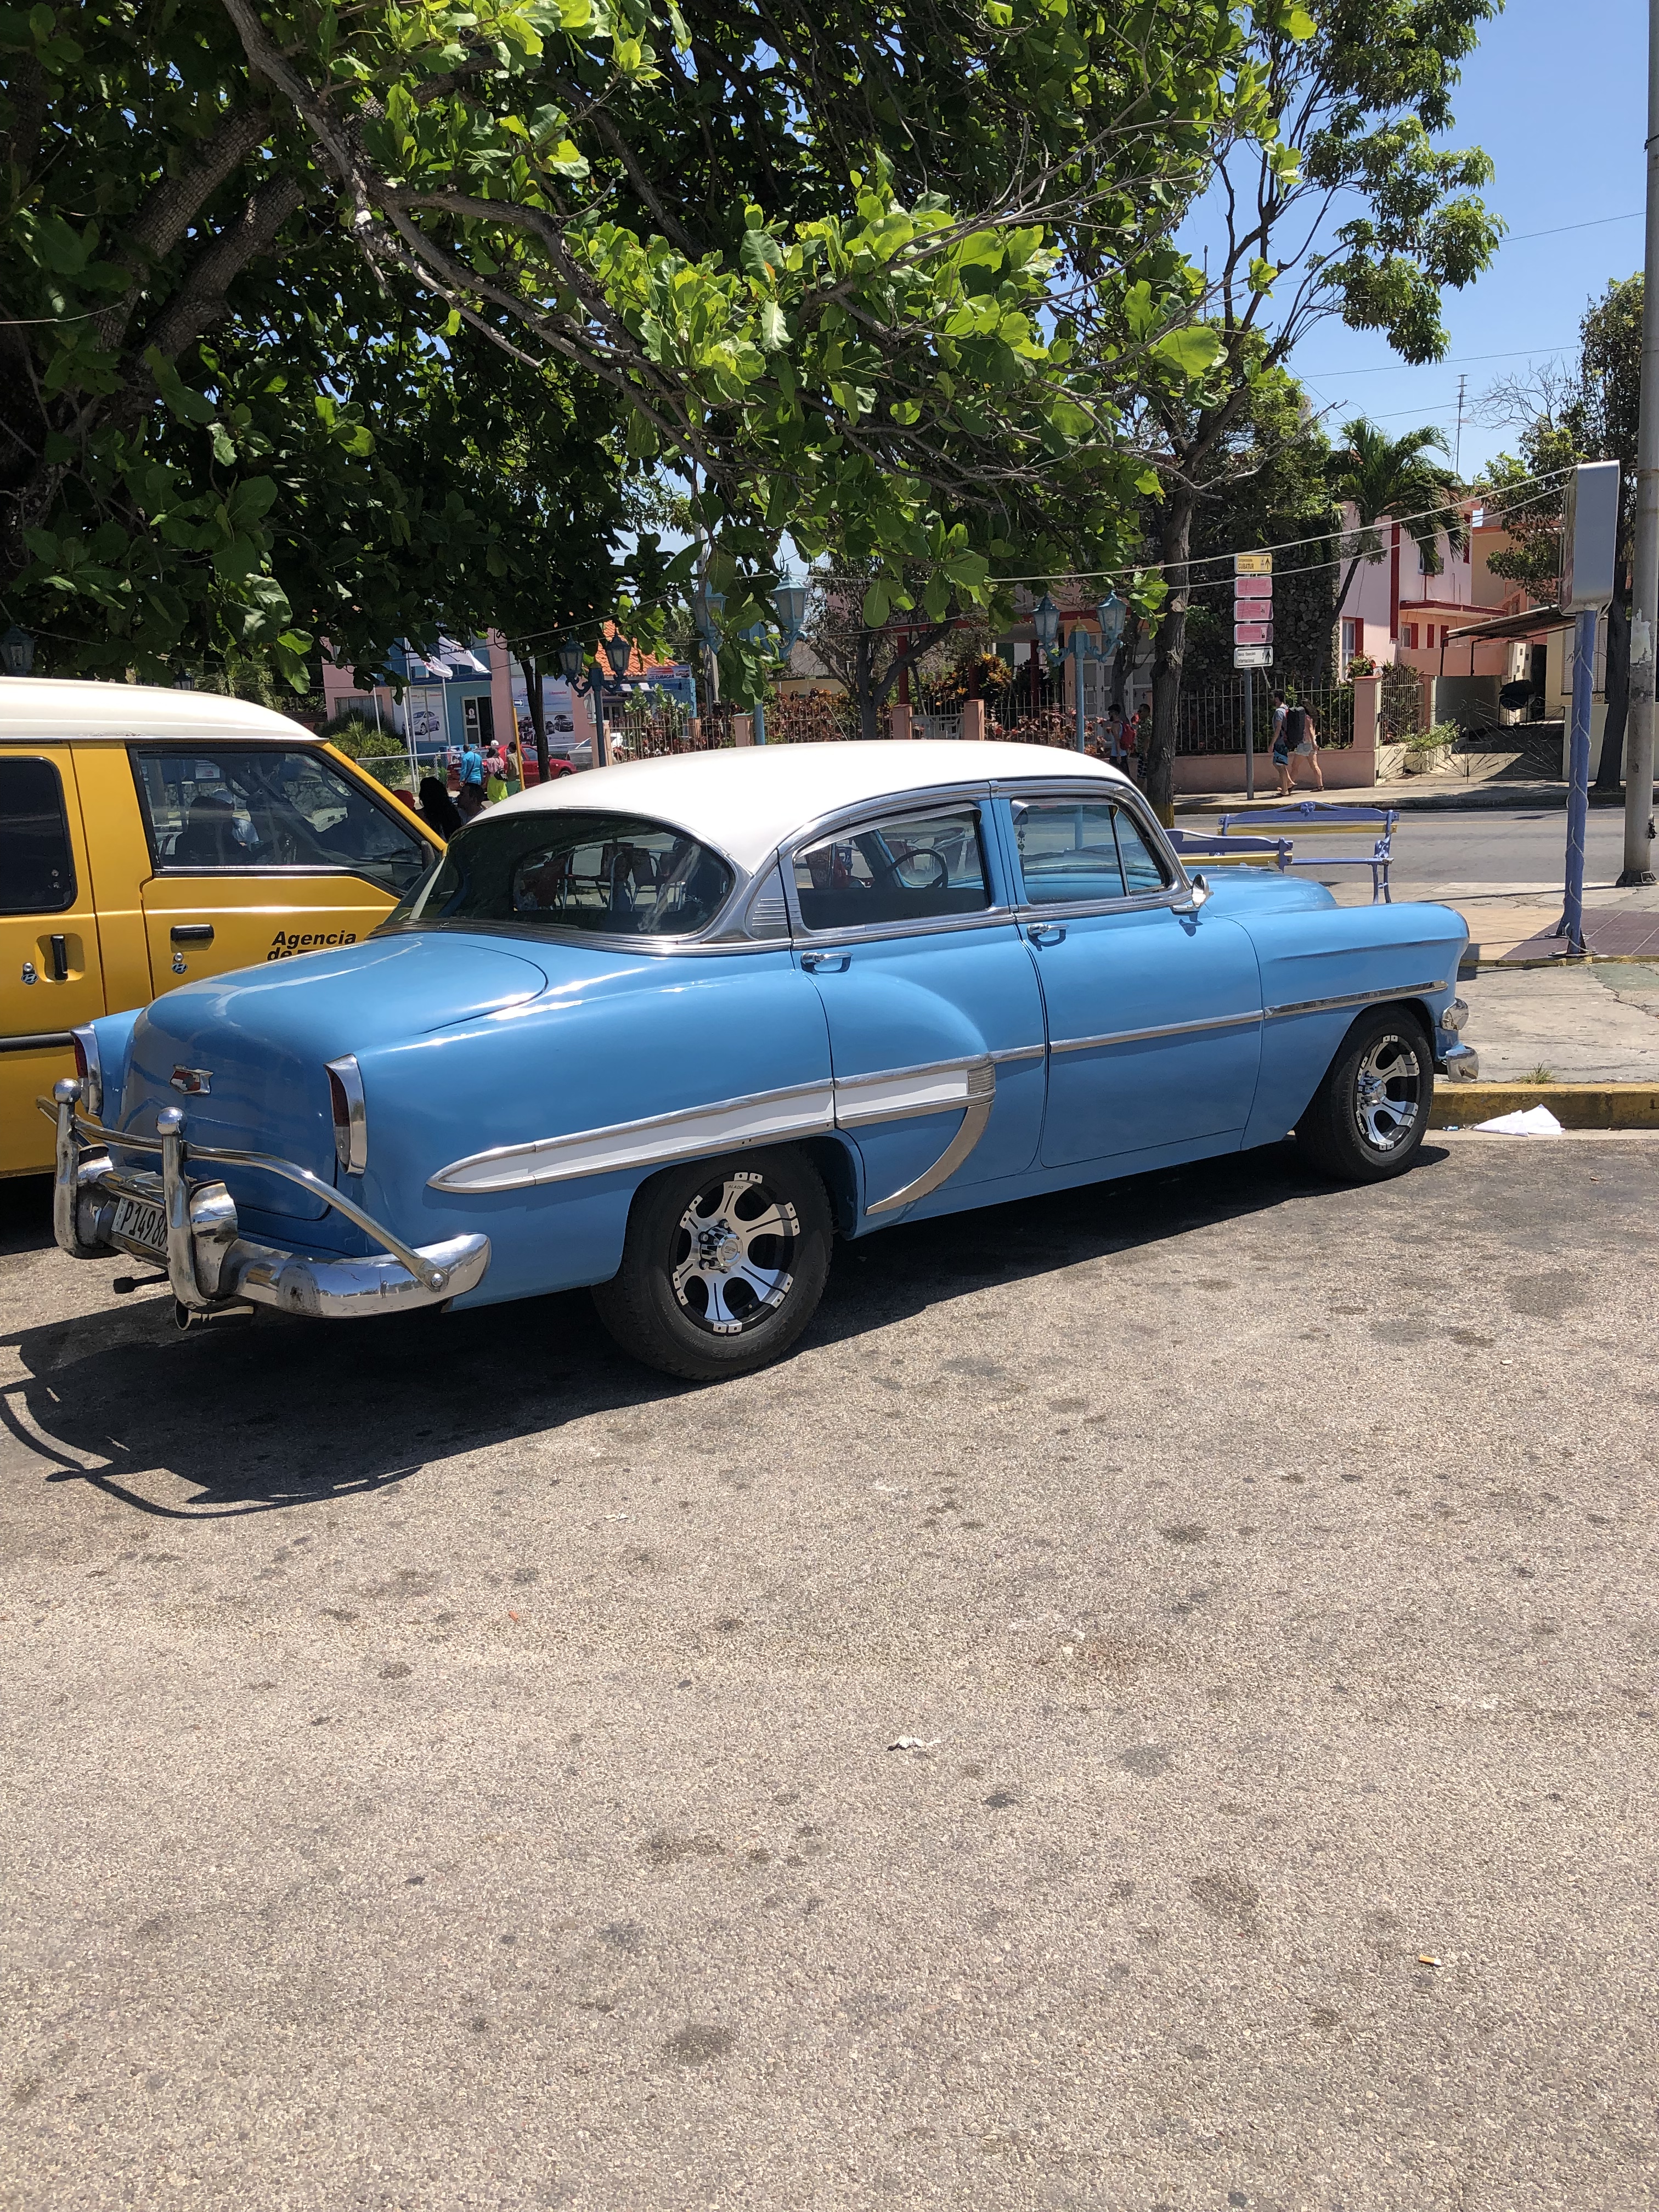



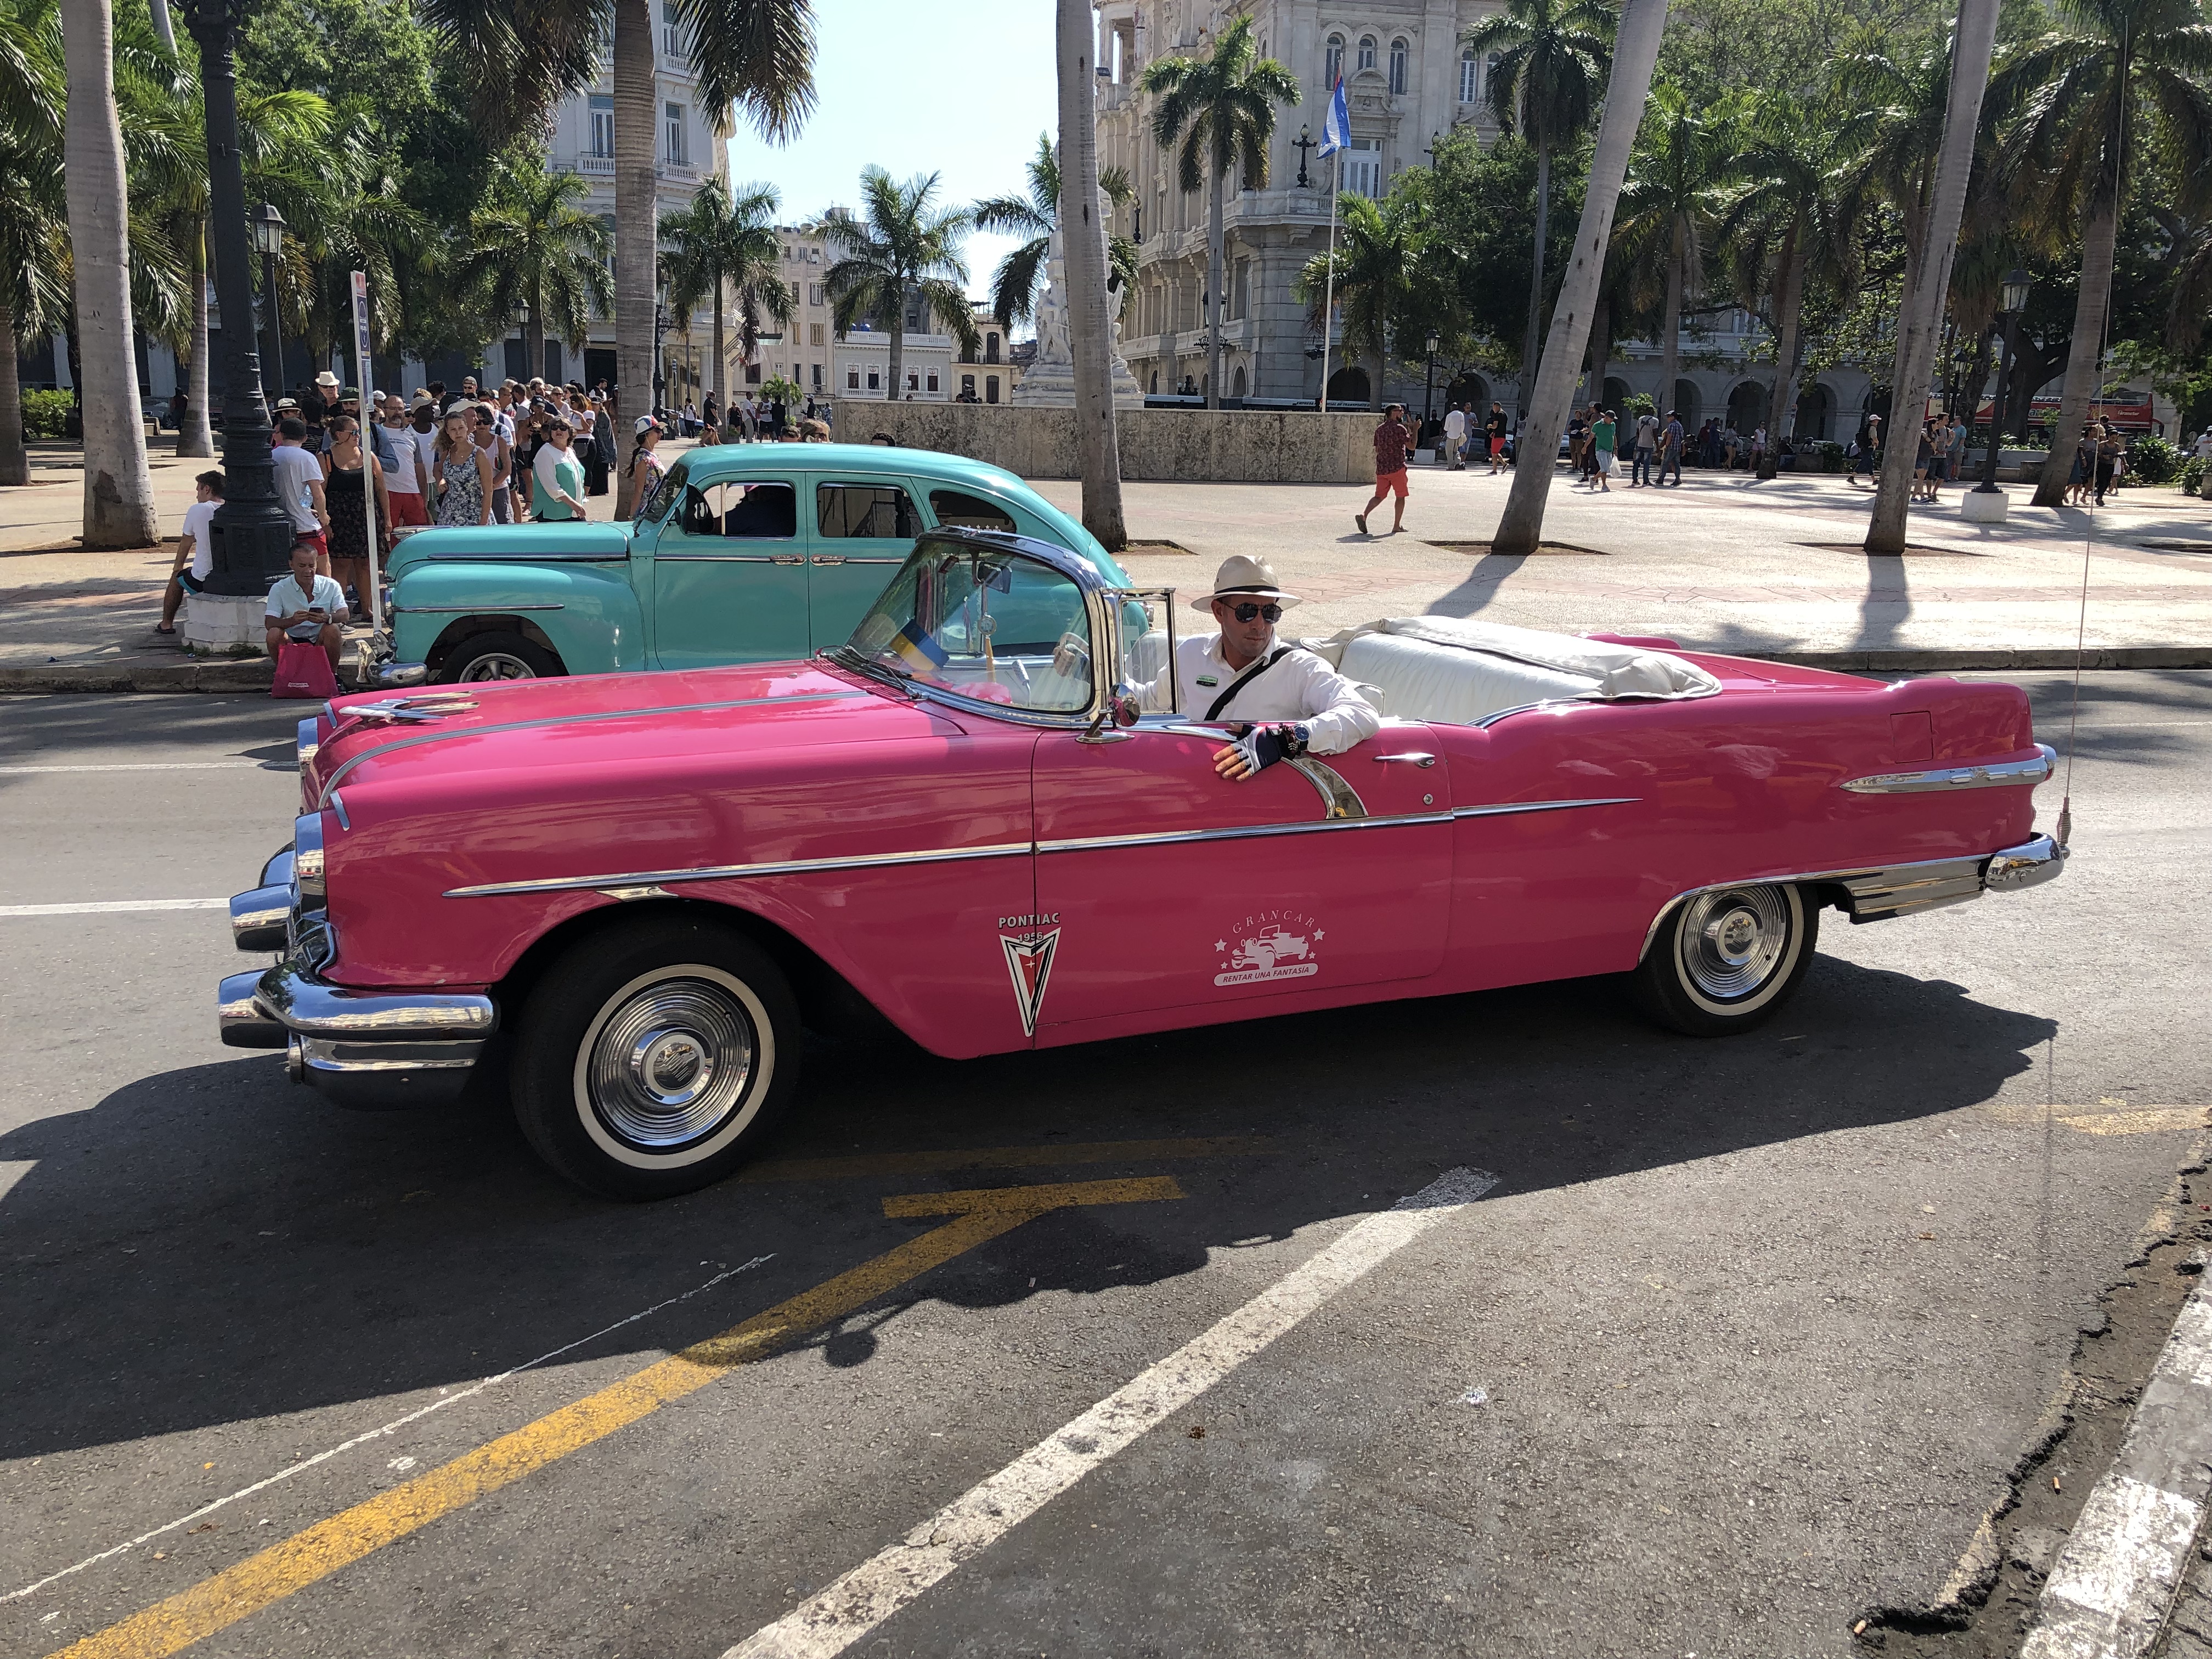


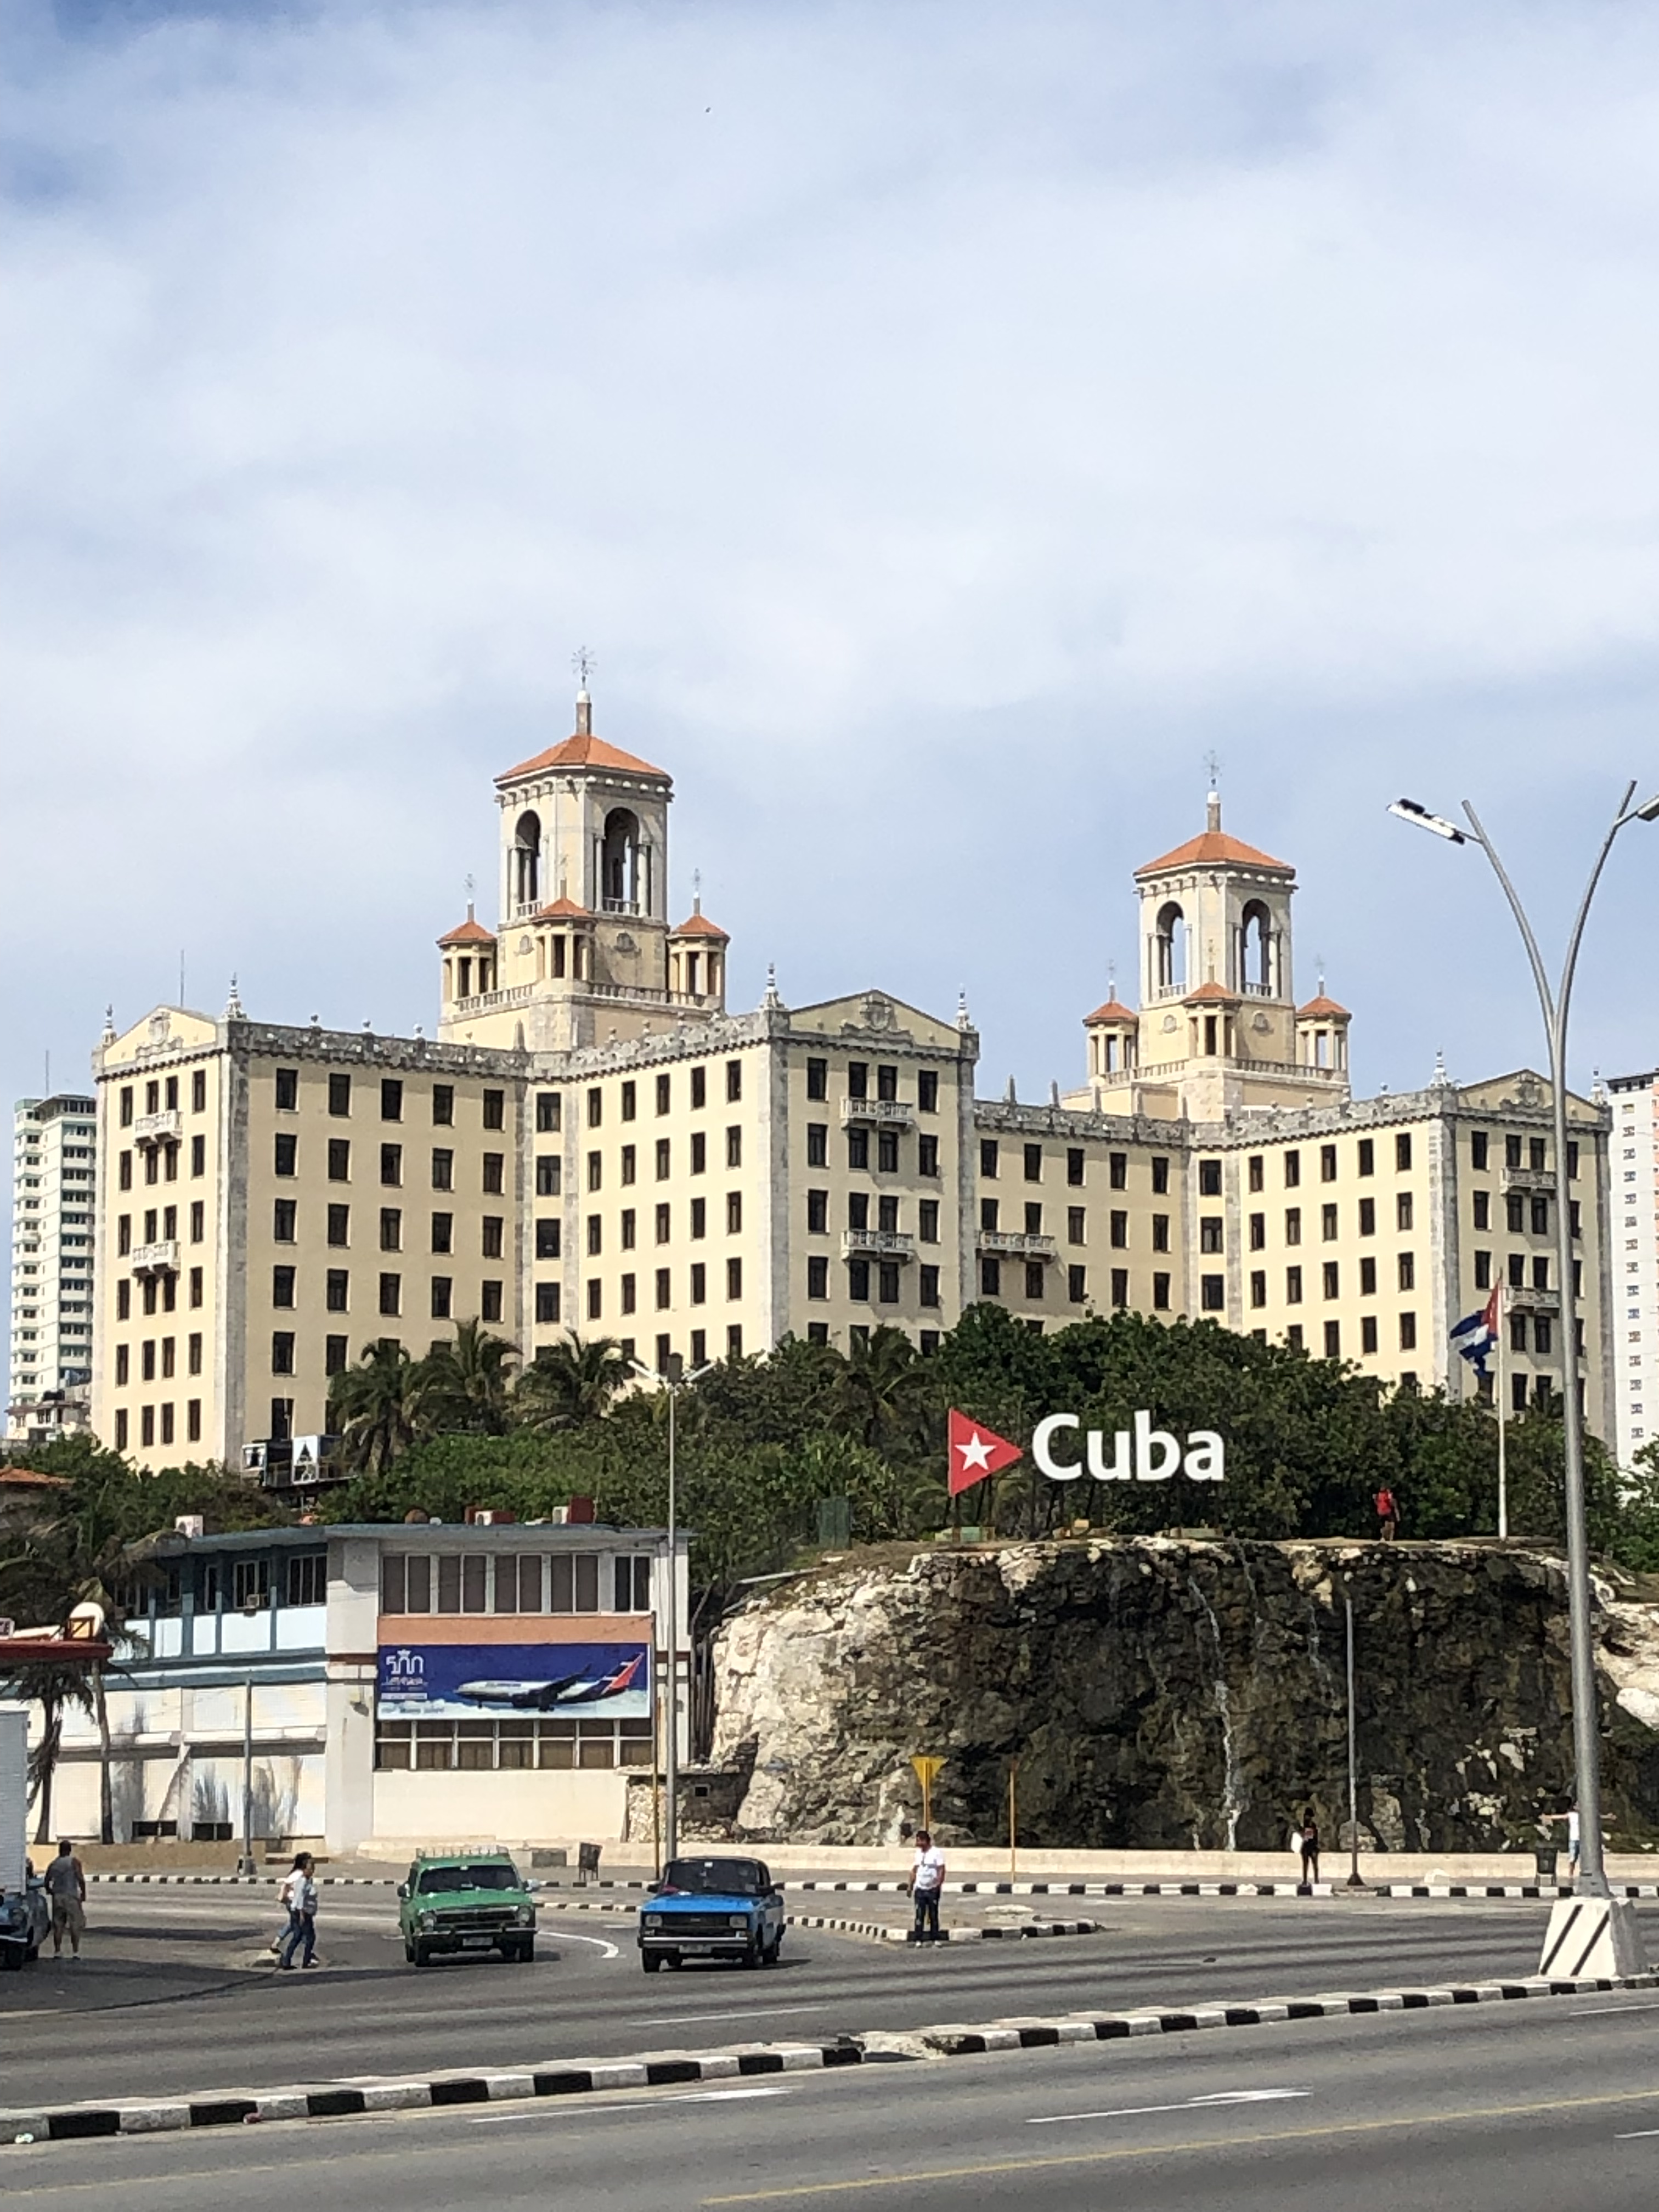


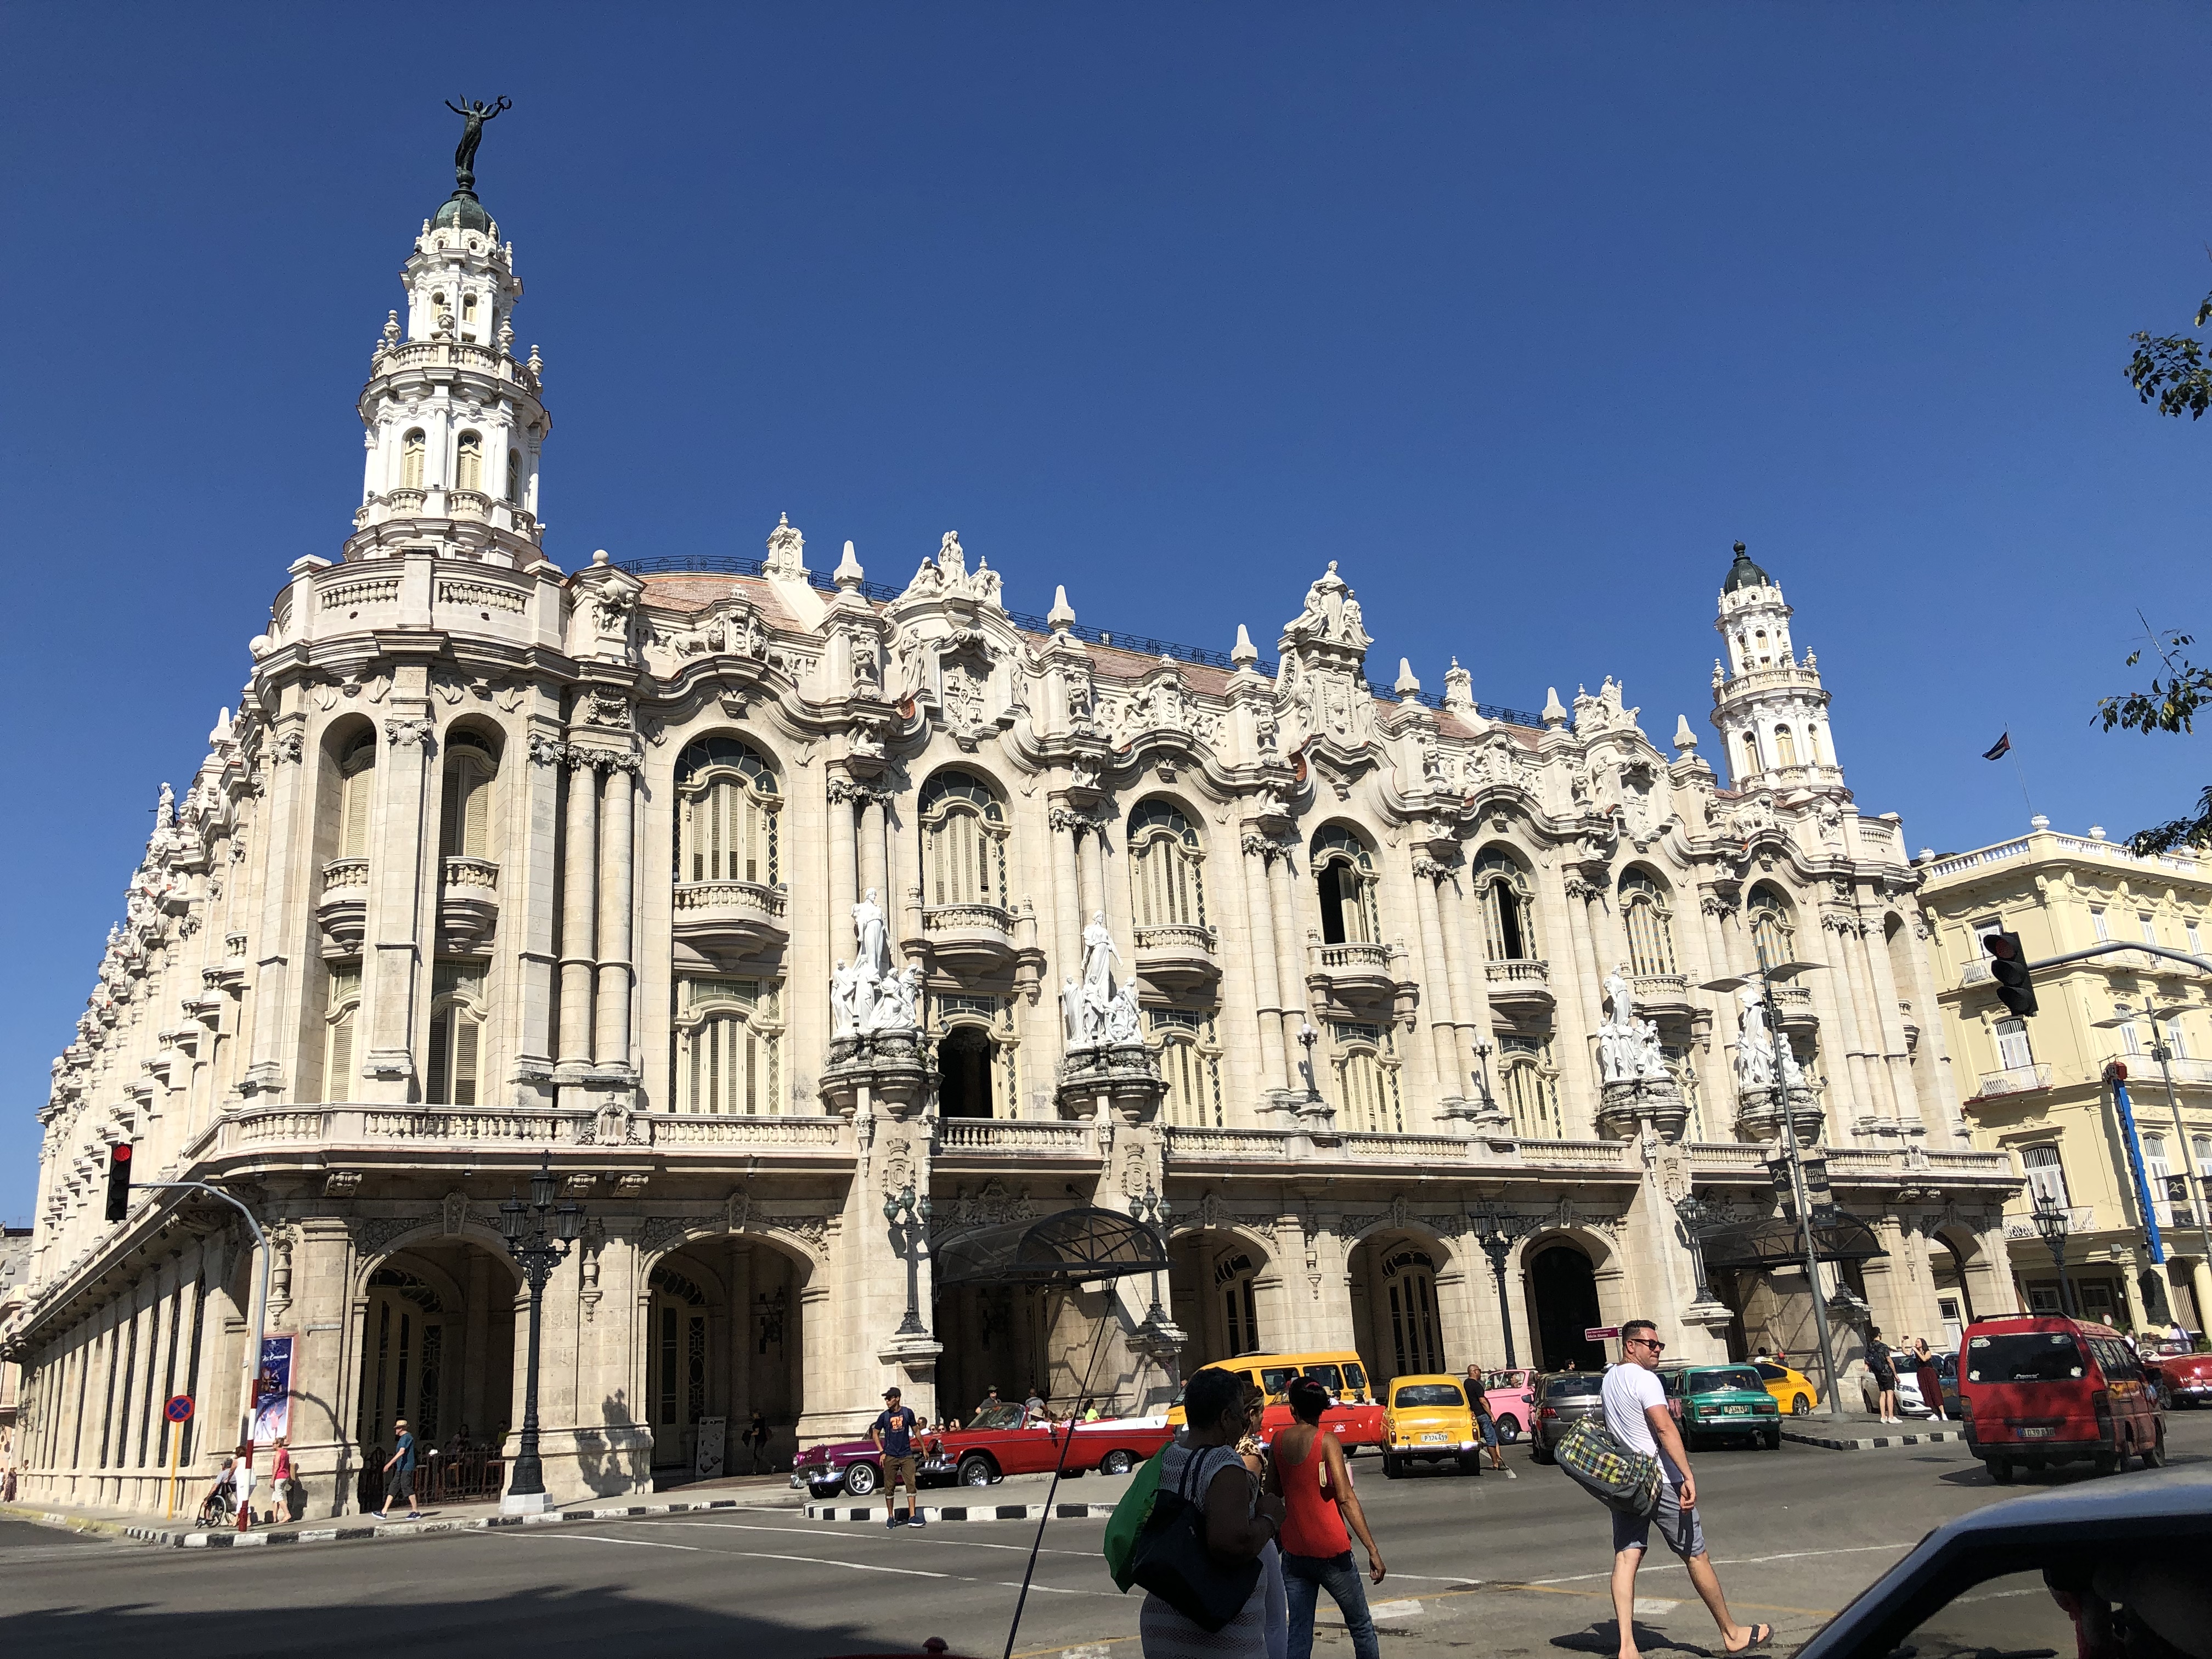





























 Enter into the equation two new players…Jeremy and Claudia. New for you, but long term friends of ours. Jeremy and I first met in our late teens when we played rugby against, and later with, each other. Decades of interactions has seen us both simultaneously and interchangeably embrace the title of “Jimmy Lau Lau”. This title started as some rubbish spoken in a bar has endured for over 30 years. So with our respective birthdays only a month apart…so began the notion of “Jimmy and Jimmy’s Caribbean vacation”.


 And this is what we found… We stayed in a manager’s unit that was centrally located within a retirement village above “the clubhouse”. They are not called retirement villages but rather they are independent living units but for my purposes retirement village works just fine. In reality it was a suburb of about 160 townhouses surrounding a centralised community area. Each townhouse was freestanding, fully independent and spectacularly maintained and the communal area had the clubhouse that contained a gym, library, pool, bowling green, putt putt course, pool table, art and craft rooms, an industrial kitchen and heaps of dining and recreation space.


 Anyway…I found us a place to live a job for me. Our home is walking distance to everything the CBD has to offer and has a restaurant strip walking distance in the other direction. We are about 250 meters from the Swan River as the crow flies and half way across the the river is Heirisson Island (a landscaped nature reserve) that contains a mob of Western Grey Kangaroos. This is a favourite for tourists as it is a leisurely 2km circuit walk around the island and you are almost guaranteed to see the roos.


 and match day followed by a hangi (native NZ Maori pit cooking). For those that do not know the Hangi involves digging a pit in the ground, heating the stones in the pit with a large fire, placing baskets of meat and veg on top of the stones, and covering everything with earth for several hours before uncovering. Boof and I first did this together many years earlier when I stood next to him at their wedding. The reality is that his Kiwi mates have the skills and we were little more than labour…nothing has changed…however even the labour level reduced this time around.


 Back on the road the next morning and we ripped out another 924 kms to the South Australian town of Streaky Bay. On the West Coast of the Eyre Peninsula in South Australia, Streaky Bay is a stunning spot with three stunning scenic drives covering this section of the Great Australian Bight: Westall Way Loop, Cape Bauer Loop and the Point Labatt Sea Lion Scenic Drive. So we stayed at the pub for a couple of nights. Overlooking the water and jetty, ate good food, relatively well priced, wandered the streets, admired the old school stone buildings, did the tourist drives and had what was becoming an all too familiar conversation.


